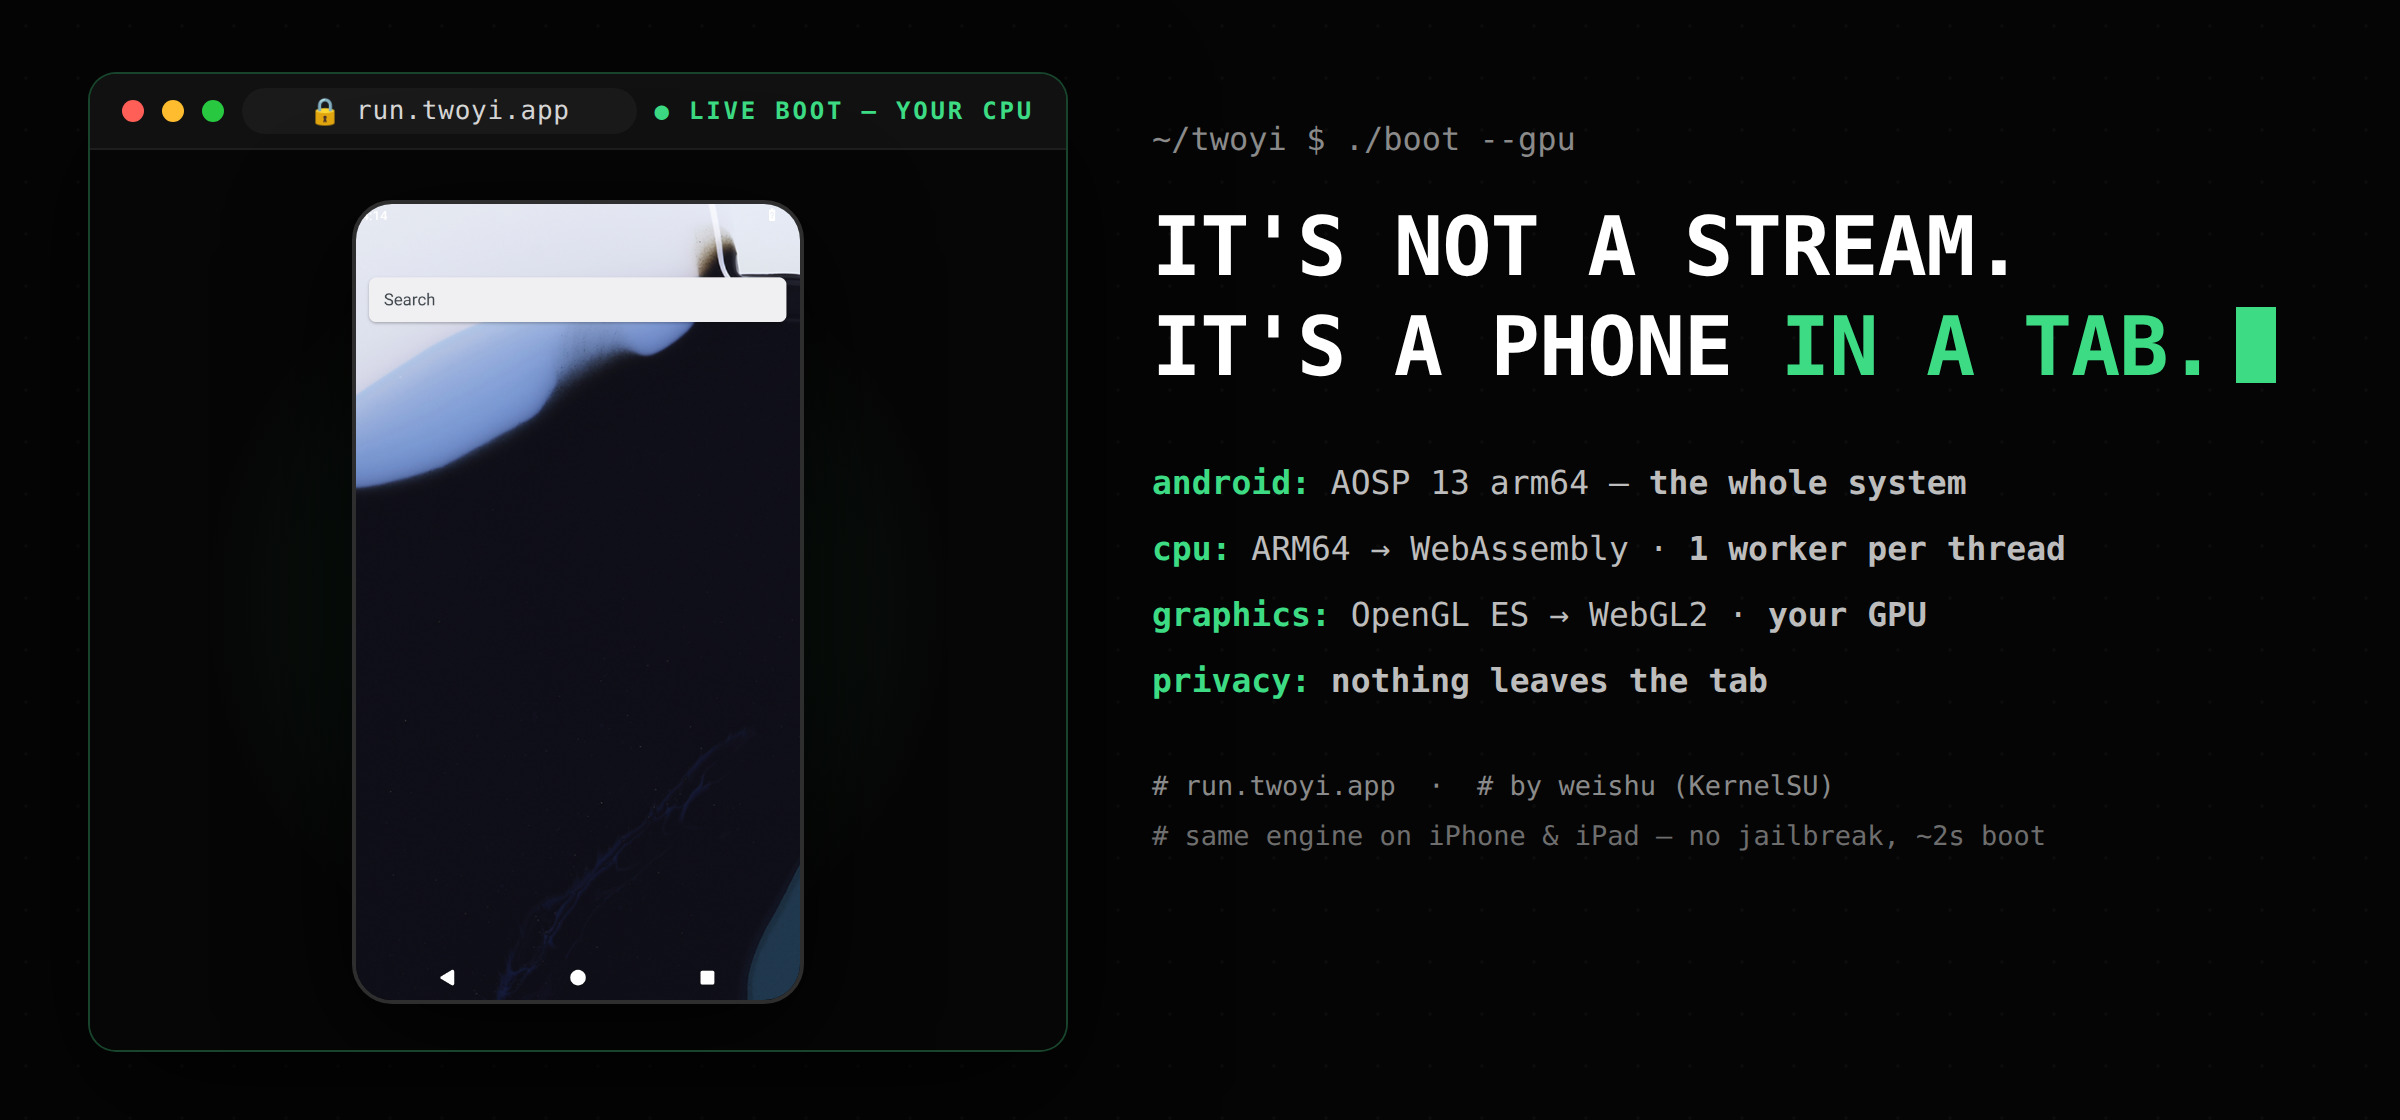
A WHOLE ANDROID 13 IN A TAB — AND THE URL IS PULL-PROOF
It boots on your own CPU in about ten seconds — nothing installed, nothing streamed, nothing rented. One URL works in desktop Chrome on a laptop, a Chromebook, even an Android phone.
 run.twoyi.app — the tab that boots Android · twoyi.app — the maker’s page, IPA + APK
Quick start — 60 seconds:
-
Open the door above in desktop Chrome → press Start — the presets are pre-loaded
-
The command box takes your own argv:
toybox sha256sum /system/build.prop→ Android runs it and prints the hash -
Hit Boot GPU → a real home screen,
720x1280, hardware-rendered -
Hand-roll the boot line:
/system/bin/sh -c 'echo hello from mksh; toybox seq 3' -
Frame nerd? Add
?framestatsto the URL → per-frame stats -
Browser menu → Install (or Add to Home Screen on a phone) → a full-screen icon, no store, no signature
Three flavours, one engine — Android’s code gets AOT-translated to real native code ahead of time, so nothing is emulated and no JIT ever runs:
| where | what you get | boot |
|---|---|---|
 browser tab |
AOSP 13 arm64 · WebGL2 · a fresh system every run | ~10s |
 iPhone / iPad |
full Android 13 · no jailbreak · 120fps ProMotion | ~2s |
 Android phone |
Android 8.1 / 13 / 17 inside one app · no root needed | ~1s |
Every run is a clean room — detonate a sketchy link, park a burner account, fake a location — the host device never touches any of it.
The street tricks — argv, clean rooms, spoofing, the AI worker
-
 The detonation chamber — every run starts factory-fresh: open the sketchy download page or APK there first, close the tab, nothing survives
-
 Burner identity — a throwaway Google account inside the tab keeps a separate fingerprint from your real machine; the whole identity dies when the tab closes
-
 GPS, camera, sensors — all virtual — the maker’s architecture docs give the container a fake location, camera feed and sensor data while your real hardware stays silent (twoyi/twoyi)
-
Twoyi Twin — the AI phone worker — one sentence and it opens apps, taps, types inside the sandbox; bring your own key (Gemini, DeepSeek, Qwen, Kimi…) and it asks before paying, deleting or posting
-
 The X-ray twin — Vetro boots unmodified AOSP 15 + microG in a tab the same way and records everything: every request in clear text, drop an APK, read its network behaviour, export HAR/pcap
-
 Root inside, soon — the maker literally wrote KernelSU; root + a module ecosystem for the sandbox is on the roadmap (“Forget SuperSU and Magisk — you’re talking to the right guy”)
-
 Tuned boots — the page ships
boot/boot-gpumodes and a720x1280@240display config; the GPU path struggles? plain boot still works
The iPhone door today — sideloads, sizes, the Android 17 rival
-
 IPA verified live — twoyi.app/ios/ →
twoyi_1.2.0_933.ipa(~590 MB — the whole Android rides inside) · Android 13 · iOS/iPadOS 15+ -
 The APK door — twoyi.app/android/ · Android 8.1 / 13 / 17 inside · needs ~4 GB free · no root, no ADB
-
 Install lanes — TrollStore = permanent on iOS ≤17.0 · SideStore = signs on-device, no computer · AltStore = free cert, re-signs every 7 days
-
 Why “no JIT” is the whole trick — QEMU/UTM translate code piece by piece at run time (a debugger attached or StikDebug); Twoyi pre-translates everything at build time → seconds to boot on chips from years back
-
 The Android 17 rival — kernarium/releases ships the real-kernel LineageOS 24 IPA on GitHub — A14+ chips, two entitlements, heavier boots
-
 The maker — github.com/tiann, creator of KernelSU + VirtualXposed; the original container repo lives on, archived (MPL-2.0)
App Store said no. The URL says yes — and it always will.
 !