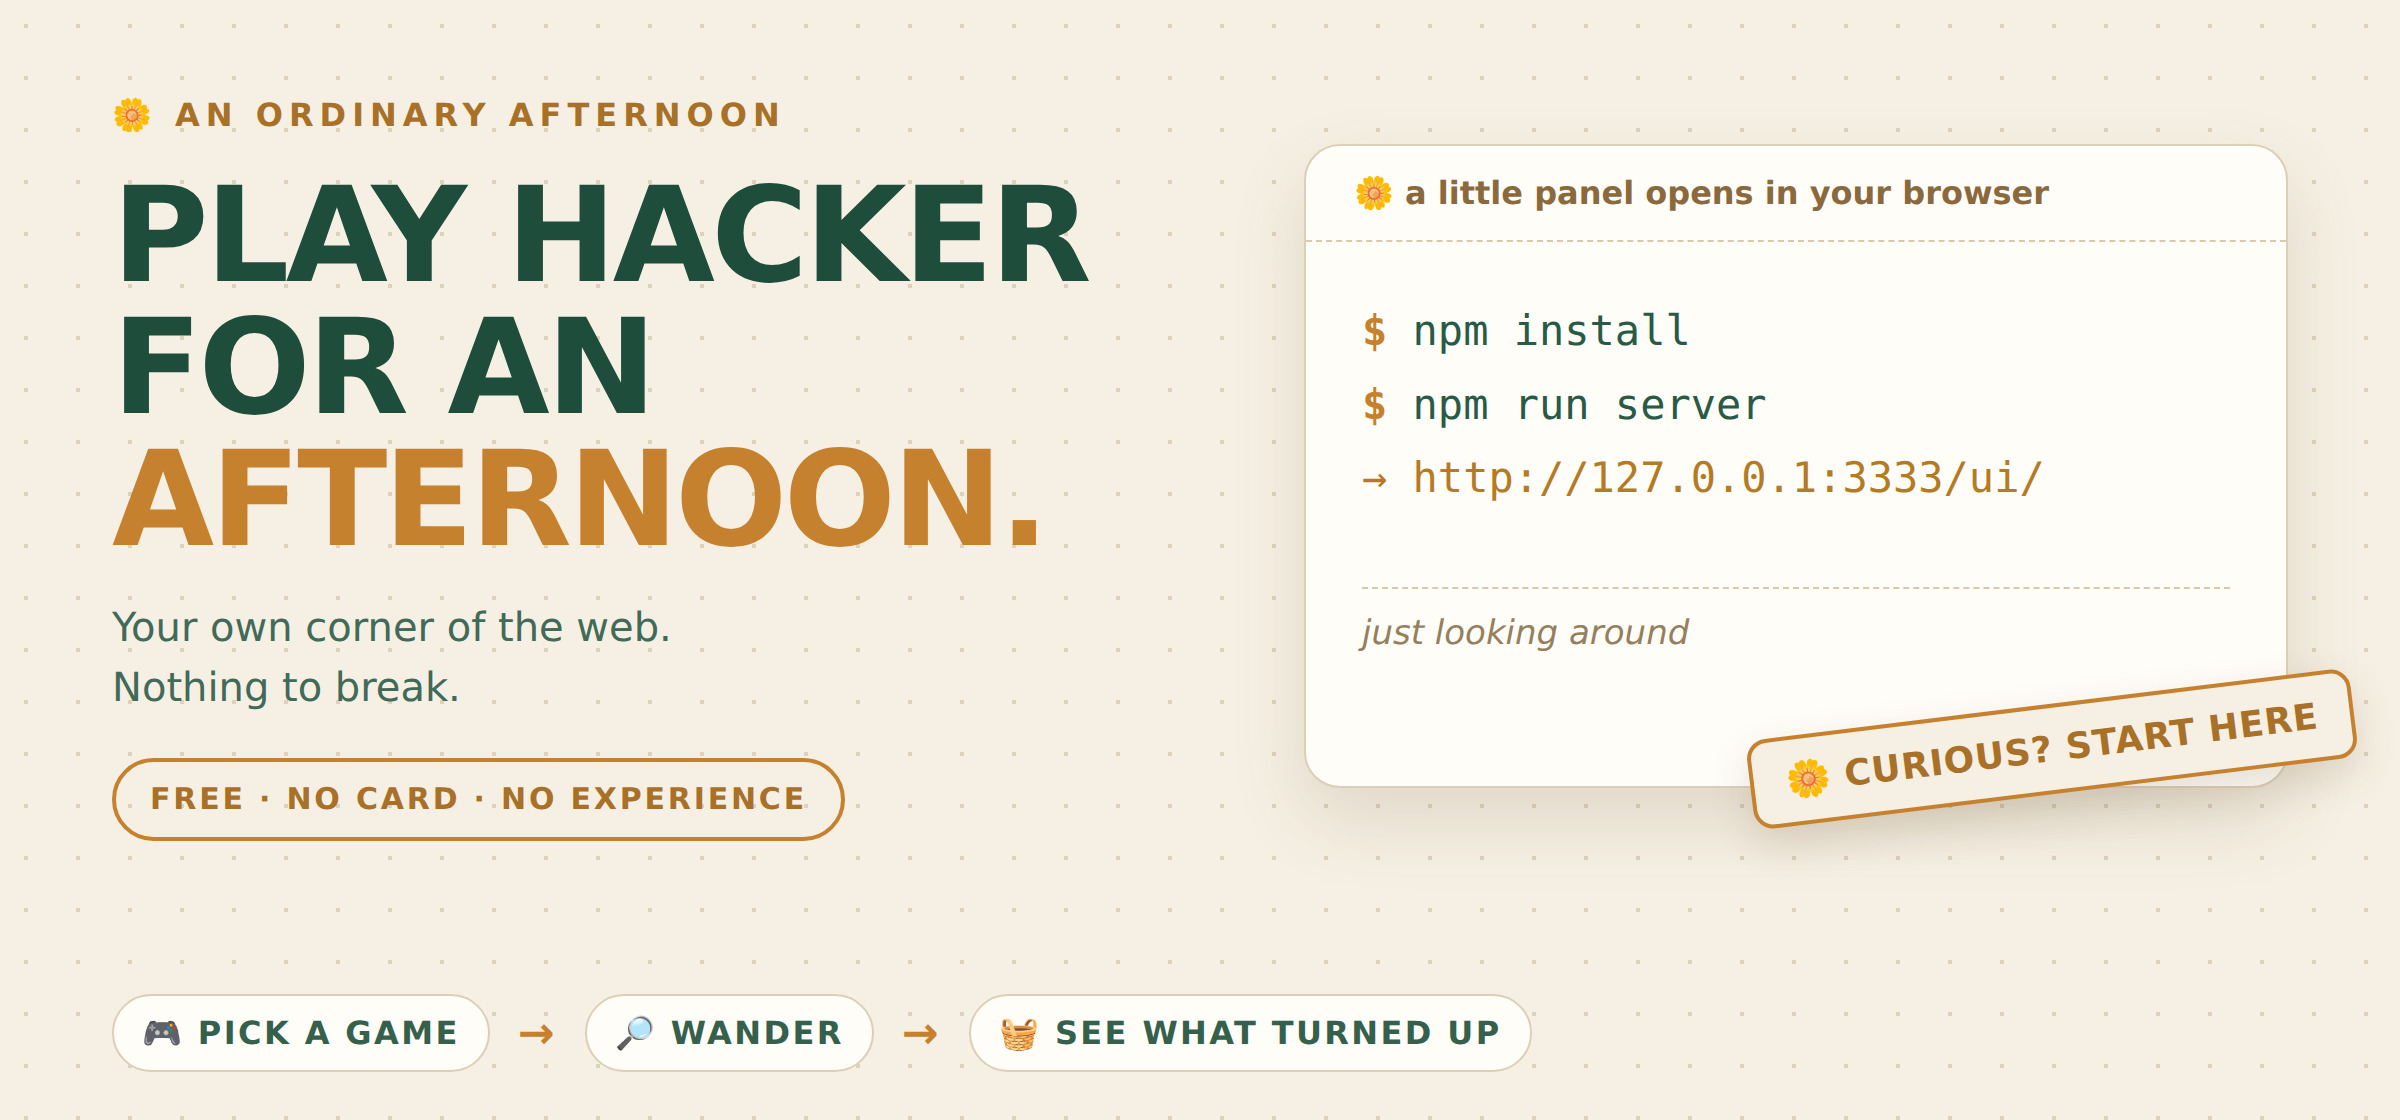
Ever wonder what a hacker would see on your site? Go look — it’s free.
An ordinary afternoon. Your own corner of the web. An AI that walks you through what it sees.
 Start somewhere safe — pick a free practice game and click around. Nothing to break.
 Then get curious — point T3MP3ST at your own site and watch it wander.
 Open what it found — see the little trail of steps behind each thing.
Want it on your own machine?
npm install
npm run server        →  http://127.0.0.1:3333/ui/
🧺 What turned up, and the little trail
- The repo — 7.1k★, AGPL-3.0, TypeScript, fully self-hosted
- verify-claims — every headline recomputed from committed artifacts,
27/27green - Integrity Ledger — every correction and re-measurement published in the open
- WHITEPAPER — the measured engine is recon, a real tool-calling loop
- XBOW’s own note — the old 104-task set is saturated; the maker re-ran the numbers in the open
- MCP guide →
security_reconbrings recon to any MCP-aware agent - OBSIDIVM bridge → 14 targets, 125 expected findings, letter grades
🛠️ For the tinkerers
- Supported helpers — the AI helper you already use, or a free local one
- HexStrike AI — 150+ security tools over MCP, hands for the recon brain
- Decepticon —
decepticon mcp serveadds full-chain agents to the same coding agent - Groq · OpenRouter free · Google AI Studio — OpenAI-compatible overflow when you bring a key
- PortSwigger labs — 190+ legal practice targets
- Certificate Transparency · OSV · ProjectDiscovery — passive recon feeds, zero traffic to the target
- HackerOne safe harbor — written cover for AI research on in-scope programs
- bounty connectors — scope-checked drafts, you click send
 Go on, be nosy.
 !