I’m currently utilising a free AI coding CLI tool, but it has tight regional constraints in my country that limit access to some features and models available in the US.
Here is what I’ve attempted so far and the challenges I run into:
-
Free US HTTP/SOCKS Proxies (Terminal Level): - Configured HTTP_PROXY / HTTPS_PROXY in my terminal.
- Result: Worked well originally — unlocked all US models and full access. However, free proxies are highly unreliable and disappear after a short time.
-
Commercial VPN (Proton VPN - US Servers):
- Set up a system-wide / CLI connection through Proton VPN.
- Result: The CLI tool’s security checks detect the VPN / Datacenter IP range and lock/limit the tool again.
Since typical VPN datacenter IPs are becoming blacklisted and public proxies drop regularly, I’m searching for a more stable, long-term alternative.
Questions: * Has anyone successfully bypassed rigorous IP/VPN detection for CLI tools?
-
Would routing traffic via Cloudflare WARP (or putting up an SSH/SOCKS tunnel using a free-tier cloud instance like Oracle Always Free or GCP) help prevent datacenter IP flags? * Are there lightweight routing tools (e.g., proxychains, gost, or bespoke SOCKS5 bridges) that perform effectively for terminal traffic without having dedicated paying residential proxies?
Thanks in advance for any suggestions or setup guidance!
![]()
![]()
![]()
![]()
![]()
![]()
![]()
![]()
![]()
![]()
![]()
![]()
You already found the real problem: chasing a cleaner IP is a losing arms race — every VPN/datacenter range gets blacklisted, which is exactly why Proton re-locks you. So stop feeding the check a better IP. Three ways to actually win, easiest → hardest — try them in this order.
①  Dissolve it — make your IP irrelevant (try this first)
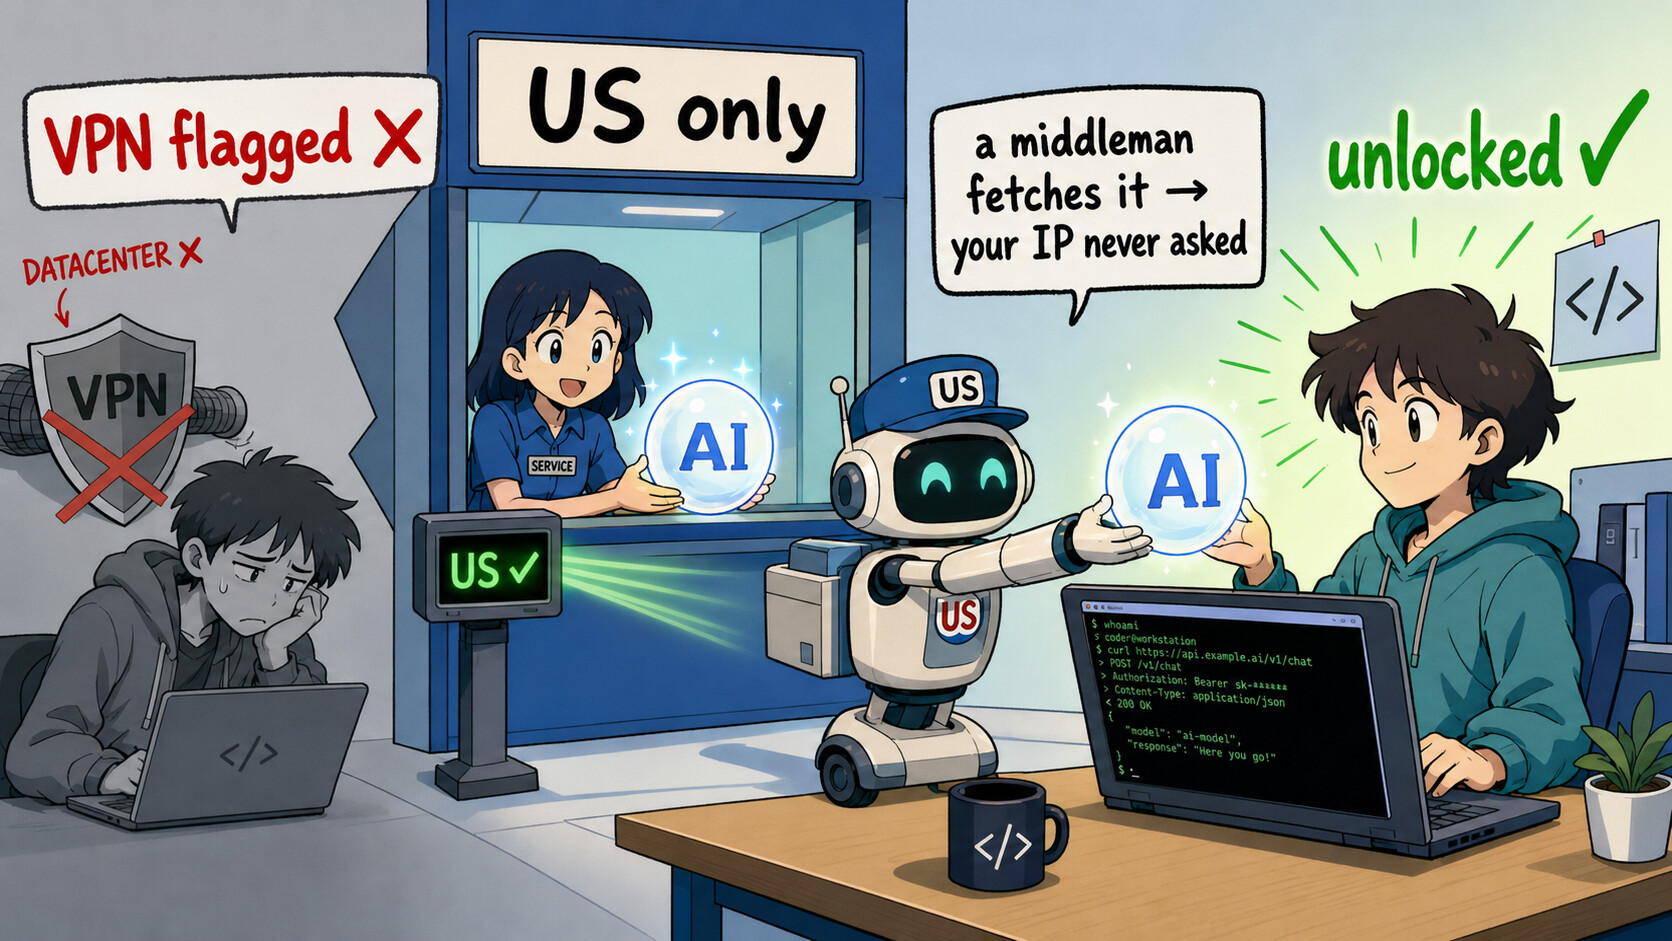
The lock only checks the IP hitting the vendor’s endpoint. Point the CLI at a middle-man that serves the models itself, and your real IP never touches the locked API:
# zero setup — OpenRouter runs the US models; you just call an aggregator
export OPENAI_BASE_URL=https://openrouter.ai/api/v1     # Claude Code → ANTHROPIC_BASE_URL
export OPENAI_API_KEY=sk-or-...                          #  ':free' models = $0
 OpenRouter — hosted, nothing to run, IP-irrelevant.
- CLIProxyAPI (45k★) —
docker run it, OAuth-login your Gemini-CLI / Codex / Claude-Code / Qwen account once → it re-serves them locally. Requests ride the vendor’s own session, so there’s no proxy signature to flag — the sharpest fit for your exact case.
- Self-host on a free HF Space or a $4 US box: LiteLLM · new-api (emits native Claude/Gemini format, drops in front of those CLIs) · one-api.
②  If you must egress — ride a CLEAN IP, not a datacenter one
Mobile & home-ISP IPs almost never carry the datacenter/VPN tag Proton does:
# an old US phone = your exit → mobile-carrier ASN, the hardest thing to flag
#   Every Proxy (tap to run)   OR   Termux:  pkg install microsocks && microsocks -p 1080
export ALL_PROXY=socks5://<us-phone-ip>:1080
③  Still on a VPS? Disguise the tunnel as ordinary browsing
Make the transport look like a real HTTPS visit to a real site — this defeats DPI and the “this is a tunnel” heuristic:
# REALITY borrows a real site's TLS handshake (dest=www.microsoft.com) — no fake cert/SNI to flag
bash <(curl -fsSL https://get.hy2.sh/)      # Hysteria2, one-line install
- Xray-REALITY + the REALITY dest picker · Hysteria2 (QUIC-as-HTTP/3, brute-forces lossy links) · sing-box (swap protocols by editing one config block) · ShadowTLS.
 Bare VPS → running node in one command: 233boy or fscarmen (REALITY by default, prints the client config).
 Disguise ≠ clean IP — still put a clean exit last (chain:
CLI → REALITY → VPS → WARP).
🔧 Make it stick on a stubborn CLI + PROVE the exit passes before you trust it
Force a CLI that ignores HTTP_PROXY through your exit:
- graftcp —
graftcp your-cli redirects that one program’s TCP via ptrace; works on the static Go/Node binaries where proxychains silently does nothing.
- tun2proxy —
sudo tun2proxy-bin --setup --proxy socks5://127.0.0.1:1080 drags every connection through at the IP layer. Also gost (wss-over-TLS disguise + last-hop), tailsocks, tun2socks, redsocks, mihomo.
Test the exit BEFORE spending a login attempt (this is what stops the proxy-death loop):
- spur.us/context/<ip> — the same residential/VPN/datacenter tag the anti-VPN vendors license. Clean residential = passes; DATACENTER = why Proton re-locked you.
- IP.Check.Place —
bash <(curl -Ls https://IP.Check.Place) scores your exit across IPQS/Scamalytics/IPinfo/AbuseIPDB at once · ping0.cc (native vs datacenter).
See exactly what locks you → then spoof only that:
- mitmproxy — proxy the CLI through it (
HTTPS_PROXY + its CA), watch for the region-check request/IP-lookup, patch that one field. Easier on Linux: HTTP Toolkit (one-click intercept-terminal).
🛰️ Free serverless relays (clean-ish US IP, honest caveats)
- deno-api-proxy — paste
main.ts into a Deno Deploy playground → xxx.deno.dev as your base-URL (built for blocked regions) · Val Town proxy (Remix → instant endpoint) · cloudflare-llm-proxy (wrangler deploy).
- Caveats: Cloudflare Workers exit at the PoP nearest YOU (region can echo your location); Vercel = AWS datacenter IPs (pair with WARP if the lock blocks hosting). Deno’s Google-Cloud IPs read cleanest of the three.
A region lock is a question about your IP. The move isn’t a better answer — it’s changing the question so your IP never gets asked.
 !