I want to know more about myself: my personal information, my fingerprints, my name, pictures of me, and all the other information I can find about me. This is to prevent a data leak or anything like that. I’d prefer general advice, since I see many of you are from the US, India, and other countries (I’m in Mexico). So, if you have any resources for obtaining my fingerprints and other data to ensure I don’t have unwanted information floating around, please let me know.
You can’t find your “fingerprint” in one search — your footprint sits in layers, and each layer has its own lookup and its own delete button. So do one clean pass: find → remove → then set alerts so new leaks ping you instead of you re-hunting forever. And since you’re in Mexico, you’ve got legal delete-levers most guides never mention. (You’ll be feeding your own data into these — so lean on the on-device / no-log ones; crop face photos; don’t sign in to the sketchy sites.)
1 — Find yourself (free, no-code, start here)
Have I Been Pwned — your email → every breach it’s in (then change those exact passwords). Doesn’t store your search.
Intelligence X — search your email / phone / CURP / RFC across leaks + dark-web dumps; surfaces LatAm/Mexican dumps HIBP misses.
Epieos — paste your email → what a stranger instantly learns: linked Google name + photo, Maps reviews, 120+ sites you’re registered on. Silent.
Your face/photos: PimEyes (true face search) · FaceCheck.ID (catches impersonation accounts) · Yandex Images (best free face matcher) · TinEye (who posted your pic first).
Google “Results about you” — your name/phone/address → Search hits + one-click removal in the same tool. Optery free scan shows screenshots of which broker sites list you.
3 — Your Mexico-only levers (the gems no US guide has)
ARCO rights (LFPDPPP) — legally force any company to delete your data (“Cancelación/Oposición”) through their aviso de privacidad; they must answer in ~20 days. Ignored? Free complaint to the SABG (the authority that replaced INAI).
Dateas — the big LatAm broker republishing your Mexican public records → search yourself, then its free “Baja de Datos” (5-day delete).
Mexico has TWO credit bureaus — pull both free reports + turn on their alerts as an identity-theft canary if leaked INE/CURP data gets used: Buró de Crédito (“Alértame”) + Círculo de Crédito. Official sites only — Condusef flags scam clones.
Ley Olimpia — leaked intimate photos: platforms must remove on report + it’s a crime; call 089 / Policía Cibernética. · REPEP kills telemarketing from leaked phone lists · R3D tracks which national leaks (INE 93M voters, SEDENA) likely already hold your data.
🧭 Go deeper — the one-seed self-scan frameworks (map it ALL at once)
SpiderFoot — feed ONE seed (email/name/username/phone) → 200+ modules crawl breaches/social/leaks into one map, from a local point-and-click GUI. On-device, so your data stays on your machine — run this first.
🕵️ Your literal 'fingerprint' + hardening (stop getting re-found)
Test it: EFF Cover Your Tracks (your “1 in X users” score) · CreepJS (catches when private mode is lying) · BrowserLeaks (WebRTC leaks your REAL IP behind a VPN).
Lock accounts: Google Security Checkup (hunt hidden mail-forwarding rules) · passkeys · set a SIM-swap PIN/NIP + port-lock (Telcel/Movistar/AT&T MX).
🔔 Stay clean — set once, get pinged when NEW data appears
HIBP Notify Me + Mozilla Monitor (future breaches, worldwide) · Google Alerts for your name/phone/email/usernames in quotes → emailed the day a new page mentions them · then re-run the broker opt-outs each quarter (brokers re-list you).
You can’t un-print yourself from the internet — but you can read every copy, tear down what you reach, and set a bell for the rest. Investigate you before anyone else bothers to.
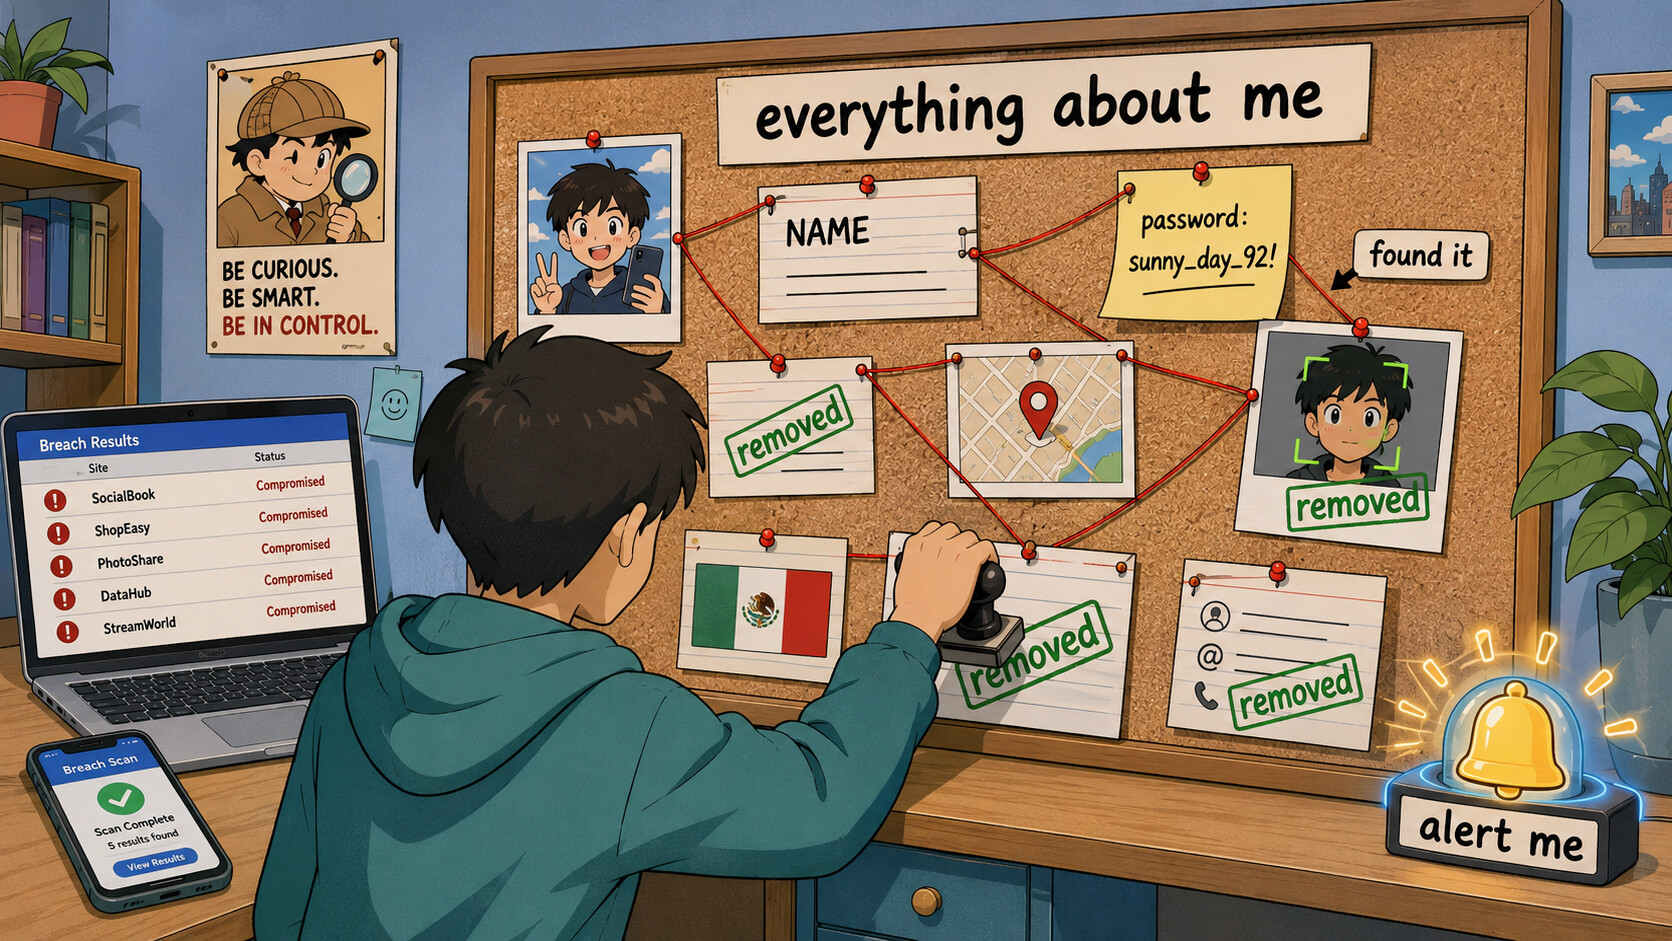
 (You’ll be feeding your own data into these — so lean on the on-device / no-log ones; crop face photos; don’t sign in to the sketchy sites.)
 1 — Find yourself (free, no-code, start here)

 Your face/photos:
 2 — Remove what you found (free)
 3 — Your Mexico-only levers (the gems no US guide has)
 Official sites only — Condusef flags scam clones.
 !