 Logitech Data Breach — 2TB of Internal Files Now Public
Hackers found backdoor → stole 2TB from Logitech → Logitech didn’t pay → everything dumped as torrent → downloading worldwide right now.
 What Happened
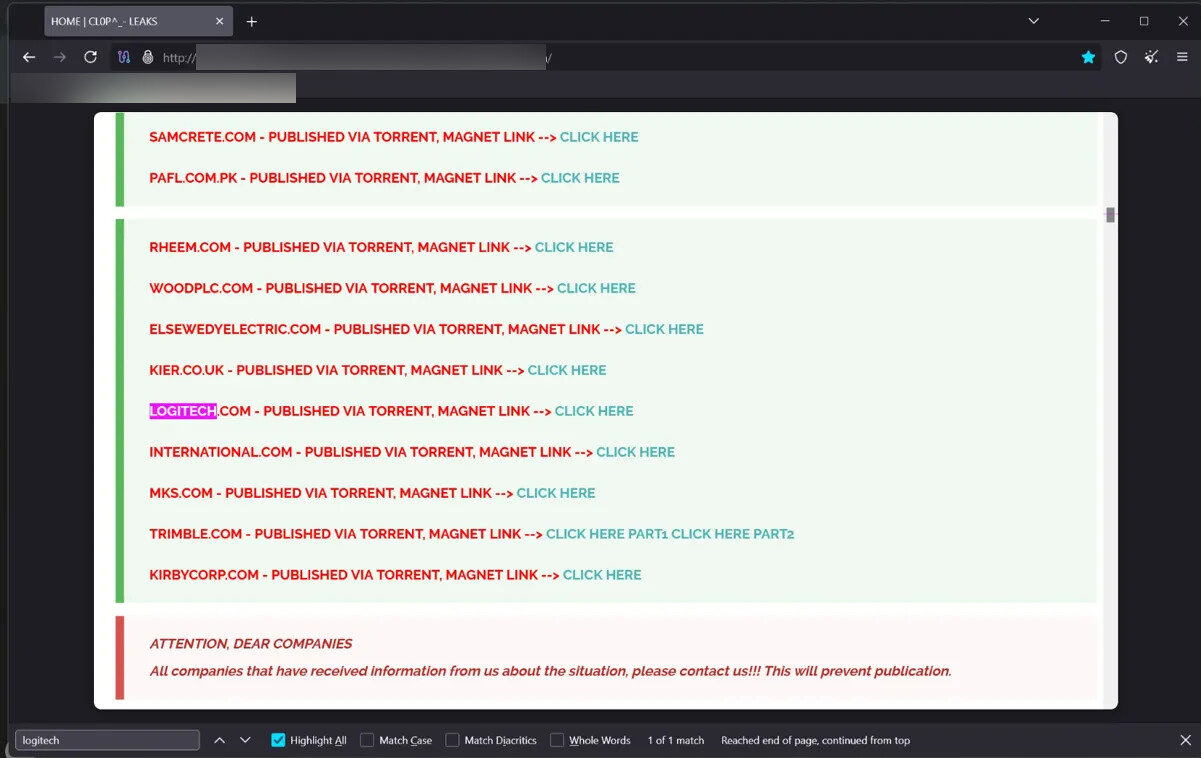
Russian hacker group Cl0p found a hole in Oracle software that Logitech uses. Snuck in August 2025, copied nearly 2TB of internal files, sent ransom demand.
Logitech’s response: nothing
Cl0p’s response: dumped everything public with the message:
“The company doesn’t care about its customers, it ignored their security!!!”
Now it’s a torrent. Anyone can grab it.
 The Numbers
| What | Details |
|---|---|
| Size | 1.79 TB |
| Stolen | August 2025 |
| Leaked | November 7, 2025 |
| Ransom paid |  No |
| Current seeds | 3 |
Washington Post leak from same hackers was 183GB. This is 10x bigger.
 File Structure (From Live Torrent)
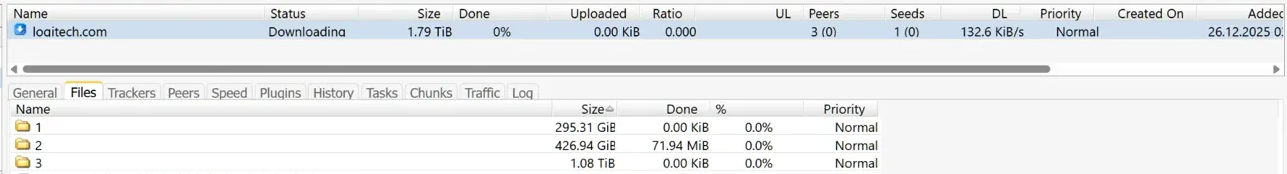
logitech.com (1.79 TiB)
├── 1/                         295.31 GiB
├── 2/                         426.94 GiB
├── 3/                         1.08 TiB
└── 42EF192A2F46D0F0A8367D8E4F92E852E89EDE46.meta    18.85 MiB
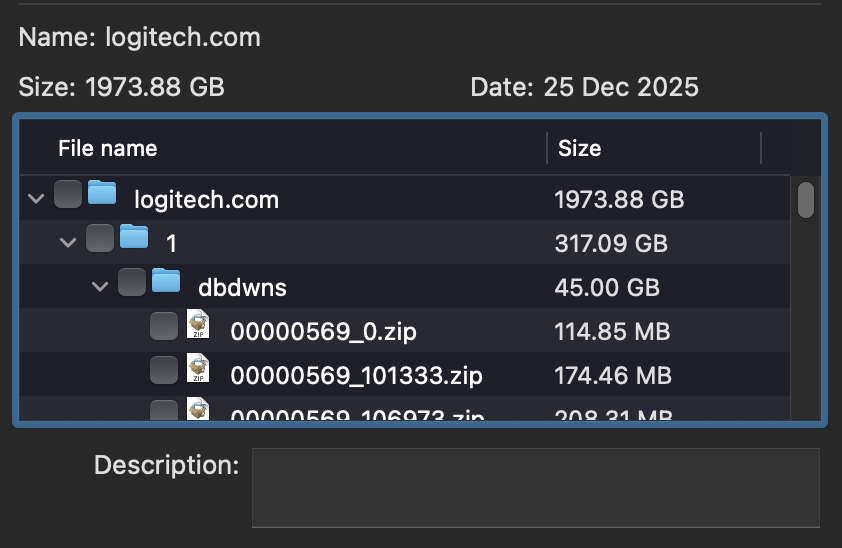
Inside the folders — Oracle database exports:
└── dbdwns/
    ├── 00000569_0.zip         114.85 MB
    ├── 00000569_101333.zip    174.46 MB
    ├── 00000569_106072.zip    209.31 MB
    └── ... (hundreds more)
Those numbered zips = Oracle EBS database dumps.
 What’s Probably Inside
Click to expand
Boring stuff:
- Invoices, purchase orders, shipping docs, inventory sheets
Interesting stuff:
- Employee info (names, emails, possibly salaries)
- Customer support tickets
- Supplier contracts and pricing
- Partner agreements
Oh shit stuff:
- Internal credentials and passwords
- Unreleased product specs
- Firmware/software dev files
- Executive emails
 Get the Leak

Size: 1.79 TB | Seeds: 3 | Status: Slow but alive
🔗 Click to Reveal Magnet Link
Hash:
42ef192a2f46d0f0a8367d8e4f92e852e89ede46
Full Magnet:
magnet:?xt=urn:btih:42ef192a2f46d0f0a8367d8e4f92e852e89ede46&dn=logitech.com
Copy → Paste into any torrent client → Wait 4 months at current speeds 
 Pro tip: More seeders = faster downloads. You know what to do.
 Other Victims (Same Hack)
50+ companies hit via same Oracle vulnerability:
 Harvard University
The Washington Post
American Airlines / Envoy Air
GlobalLogic (Hitachi)
 Schneider Electric
NHS UK
Cox Enterprises
Emerson, Pan American Silver, LKQ Corp…
All from one unpatched Oracle hole (CVE-2025-61882).
 Who Is Cl0p
- Russian-speaking group, active since 2019
- 1,100+ total victims
- $500M+ earned from ransoms
- $10M US bounty on their heads
- Their malware won’t run on Russian-language systems
Name means “bedbug” in Russian. Self-aware kings.
 Logitech’s Official Response
From their SEC filing:
“Limited information about employees and consumers… we don’t believe SSNs or credit cards were affected.”
Translation: “Please don’t sue us, we have insurance.”
 News Sources
- https://www.bleepingcomputer.com/news/security/logitech-confirms-data-breach-after-clop-extortion-attack/
- https://www.securityweek.com/logitech-confirms-data-breach-following-designation-as-oracle-hack-victim/
- https://cyberinsider.com/logitech-customer-data-exposed-in-zero-day-flaw-cyberattack/
- https://www.ransomware.live/group/clop
 If You’ve Ever
- Registered a Logitech product
- Used Logitech support
- Worked for or with Logitech
Your data might be in there somewhere. Logitech says no payment info leaked. Maybe true, maybe PR cleanup.
Last updated: December 26, 2025
Torrent status: 3 seeds, 1 peer, slow but alive

 !