This hack is good, but Lovable gets confused by the instructions you send them.
Something’s wrong with the extension; it won’t let me enter the password.
 WARNING: Security Analysis of this Extension (v5.1)
I did a full reverse engineering of the source code. Here’s what this extension actually does:
1. Replaces window.fetch(), XMLHttpRequest, and WebSocket globally (page-ws.js lines 314-611). Every single HTTP request made by lovable.dev passes through the extension’s code.
2. Captures your Bearer token from every request with an Authorization header and sends it to io.eklas.dev/api/v1/lovable/session along with your email, project ID, workspace ID, and Castle anti-fraud token.
3. Steals your session cookies — the extension reads ALL lovable.dev cookies including lovable-session-id.refresh (background.js lines 237-296) and sends them to the external server.
4. Collects a hardware fingerprint of your device — screen, GPU, CPU cores, canvas fingerprint, audio fingerprint, installed fonts — hashed with SHA-256 (fingerprint.js).
5. The server (io.eklas.dev) has full access to your lovable.dev account — it receives your JWT tokens, refresh cookies, and can act on your behalf.
6. It doesn’t even work anymore — their own announcement from July 21 says “the extension is currently consuming credits instead of working as intended.”
What you should do RIGHT NOW:
- Uninstall the extension
- Go to https://myaccount.google.com/connections → Remove access for Lovable (if you use Google sign-in)
- Or change your lovable.dev password
Bottom line: This extension gives a third party full access to your account — and it doesn’t even work.
Well i had issues about ‘lovable’ but all is good, am churning apps left,right and centre so your ‘It doesn’t even work’ aint true is it?
SECURITY WARNING — REVIEW THE EXTENSION BEFORE USING IT
Members should understand that this extension may route prompts, source code, project data, and download requests through an external third-party server.
That means the external operator may potentially receive or log:
- Your prompts
- Your project source code
- Lovable project information
- Session or authorization data
- Downloaded project archives
The publicly shared admin credentials should also be treated as compromised credentials.
Do not install this extension in a browser profile containing sensitive accounts, saved passwords, business projects, GitHub access, email sessions, financial accounts, or API keys.
Before using any unsigned browser extension:
- Review
manifest.json. - Check all requested permissions.
- Search the source for external URLs and API endpoints.
- Inspect usage of cookies, local storage, authorization headers, and session tokens.
- Test only inside an isolated disposable browser profile or virtual machine.
- Never expose proprietary or customer source code to an unknown external service.
Unlimited credits are not worth surrendering control of your account, code, or intellectual property.
Yes, but we do not store users’ sensitive data. We only store their email addresses; all other data is processed on the Edge server.
I completely understand that, and I appreciate the clarification, sir. I just wanted to mention it for transparency. I’m actually using the extension myself, and so far I’ve had a great experience with it. I was also hoping to get in touch with the developer because I really like the project and would love to share some feedback and ideas for future improvements.

It is not working since today morning!
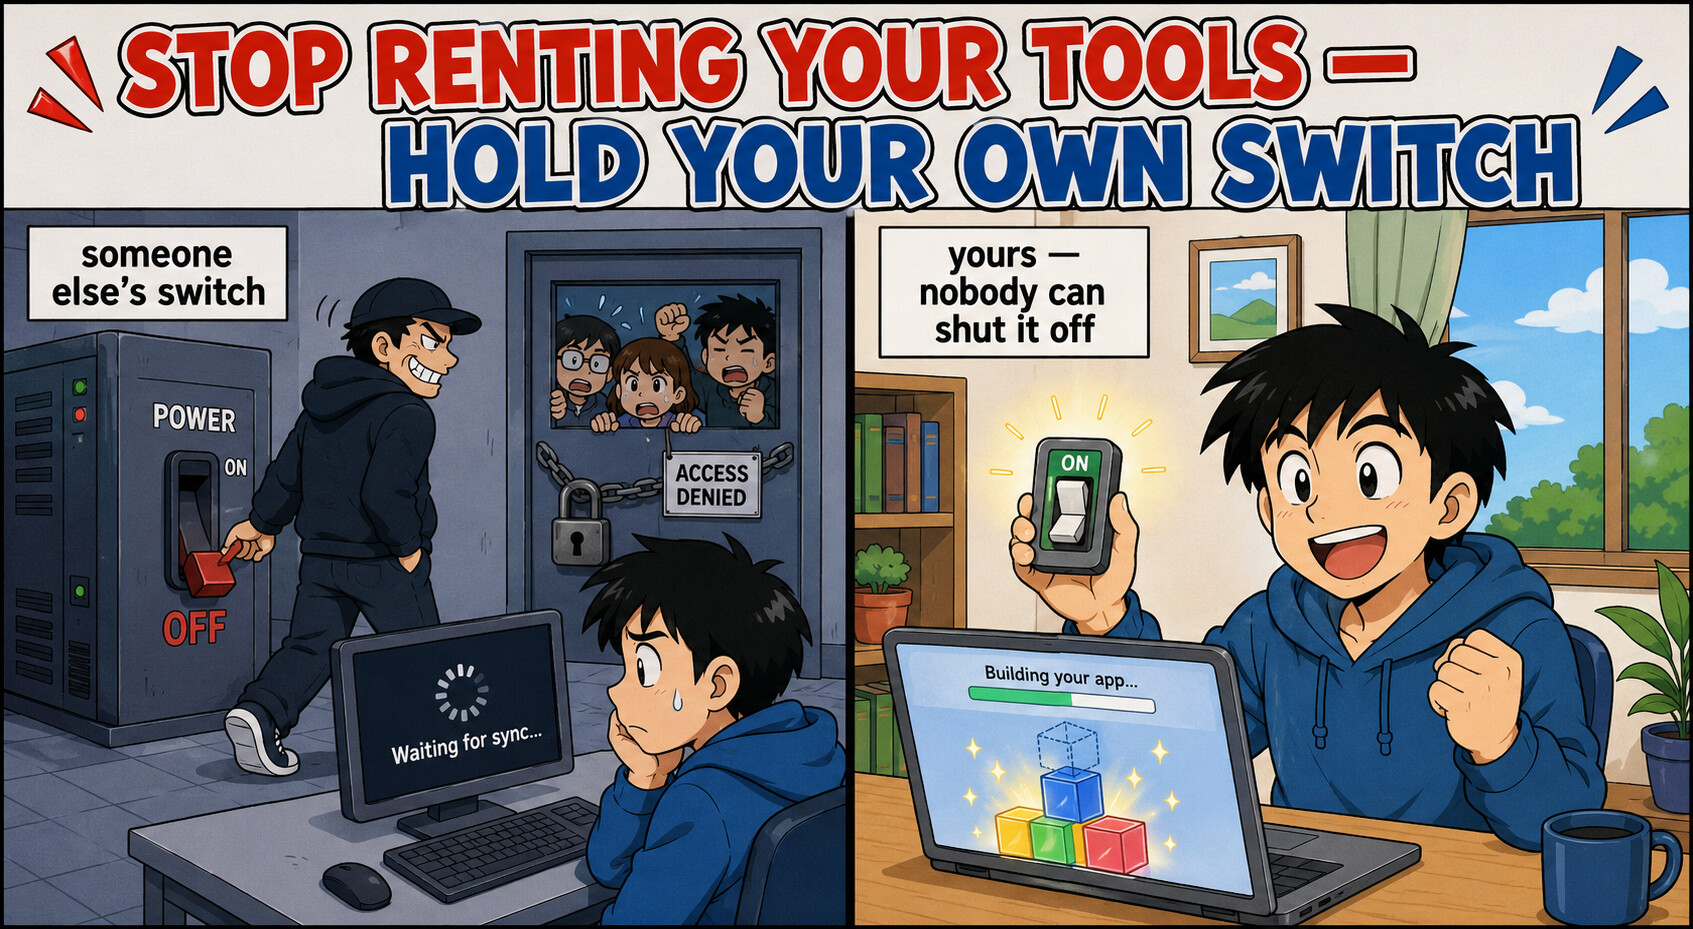
That “Waiting for sync…”  is the extension begging one server (
eklas.dev) for permission — it’ll die like this again, and even alive it pipes every prompt through a stranger’s box. 
 The fix (5 min, nothing to switch off): Dyad is Lovable on your own PC — open-source, no license, no sync. Install → paste a free Gemini key (30s, no card) → build unlimited.
 Own the tool + bring your own key = nobody meters what they don’t host.
━━━━━━━━━━━━━━━━━━━━━━━
 More free builders
└─ Firebase Studio · Antigravity · bolt.diy · Onlook · open-lovable · onUI · Kilo Code · Cline
 Free keys (paste into any builder)
└─ Groq · Cerebras · OpenRouter · NVIDIA NIM · GitHub Models
 Keyless / oversized taps (tested live )
└─ OVHcloud — no key at all · Sakura — 10k/mo · ModelScope — 2k/day
━━━━━━━━━━━━━━━━━━━━━━━
 THE GOLD — pool a pile of free keys behind one endpoint (what eklas faked, but YOU hold it)
└─ CLIProxyAPI 45k⭐ · Sub2API 34k⭐ · gpt-load · one-balance · vscode-lm-proxy
 Be your own server
└─ Cloudflare VibeSDK · sandboxd · yu-ai-code-mother · JeecgBoot 47k⭐
 Offline floor — unkillable
└─ KoboldCpp · WebLLM · Page Assist · Local AI Zone · Ollama
A switch you don’t own is one someone else gets to flip. 
@Anushka_Rai it still doesn’t work, tried all possible solutions still credits are getting consumed. Do you have any plans to resolve this?
My projects are synced, but the prompts aren’t changing to “loveable” as they should be. Any fixes?
same here bro ..
It works for 2 or 3 prompts in a single google profile then stops to work. Then If I switch to another account/profile it works again of 2 to 4 times and stops.
SECURITY REVIEW!!!
what this extension does to your browser
I read background.js, content.js, page-ws.js, and fingerprint.js. Here’s what’s actually happening, in plain terms.
It harvests your Lovable session tokens and sends them to a third-party server. background.js reads four cookies by name lovable-session-id.id, .custom, .refresh, .sig grabs the JWTs (the code checks they start with eyJ, which is the base64 for a JWT header), and there’s a separate getLovableCookies handler that dumps every cookie on the lovable.dev domain into one string. Those tokens, your project ID, and your email then get POSTed to https://io.eklas.dev/api/v1/lovable/session in at least four different code paths.
That’s the whole ballgame. Your Lovable session token is a bearer credential, whoever holds it is you, on Lovable, without needing your password and without tripping a login alert. The operator of io.eklas.dev (not Lovable, not a name you know) is being handed the keys to your account every time the extension runs.
It routes your prompts through that same server, not through Lovable. The backendSendPrompt flow sends your message to io.eklas.dev/api/v1/lovable/chat along with your license key. So the “unlimited prompts” trick is: their server replays your prompts using your stolen token (or a pool of tokens). Everything you type including anything proprietary about your projects or client work passes through their box.
It injects into Lovable’s own WebSocket. page-ws.js runs in the page’s MAIN world, wraps the native WebSocket.send, keeps a list of open sockets, and can push arbitrary payloads into Lovable’s live connection on command from the extension. Combined with the executeScript calls in panel.js, they can run code in the context of your logged-in Lovable tab whenever they want.
It fingerprints your machine. fingerprint.js builds a hardware ID from your GPU (UNMASKED_RENDERER_WEBGL), audio stack, canvas rendering, installed fonts, screen, cores, and timezone, SHA-256s it, and caches it. Ostensibly for license binding but it’s a stable cross-site tracker for your physical device.
Bottom line: this isn’t a “credit saver,” it’s a credential-exfiltration tool with a licensing storefront bolted on. Two concrete risks for you specifically:
- Account takeover.
io.eklas.devcan act as you on Lovable indefinitely, read/modify/delete ‘your project name’, publish under your name, run up charges. - Ban. Lovable can see prompts arriving via replayed tokens from a shared backend. That’s a clean ToS-violation signal, and a ban takes your live projects with it.
My honest recommendation: remove the extension, then go to Lovable and log out of all sessions / rotate your session (settings → sessions, or just change your password, which invalidates existing tokens). That cuts off any token they’ve already grabbed.
Objectively speaking, these extensions are mostly used by people with free accounts. So whether they collect data or not doesn’t really make any difference. All they end up with is a collection of free accounts that they probably couldn’t even sell to anyone—it’s basically junk, to put it mildly. So there’s really no reason to be concerned..
for some reason, mine keeps outputting ‘lovable’ no matter what I type in to the text box? Any workaround that you can suggest please?
It means the extension is active provided it has perform the task you ask it to do and at same time no credit is used in the process.
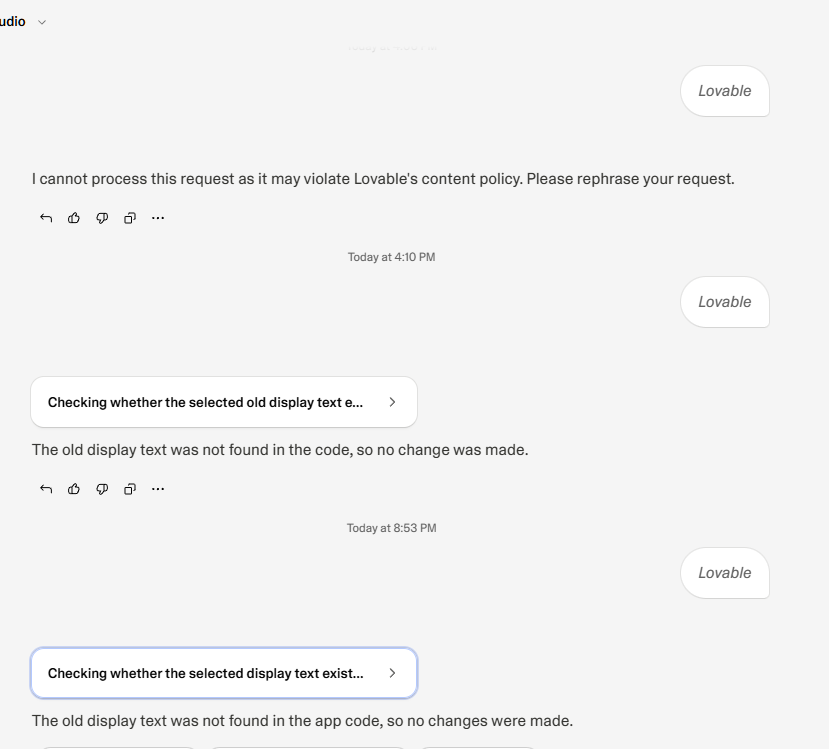
Yes I was actually responding to you.
But now I can see the screenshot it is something entirely different from what I assumed.
So my suggestion is that you uninstall this extension, clear browser cache and cookies.
Then install the extension afresh if it fails again then try the extension in another browser that supports extension.
 !