THE KEY WAS IN PIECES. THE PIECES WERE THEIRS.
Nov 6, 21:13 UTC. I’ve had this one pinned since the first notice, and the whole story sits in one question.
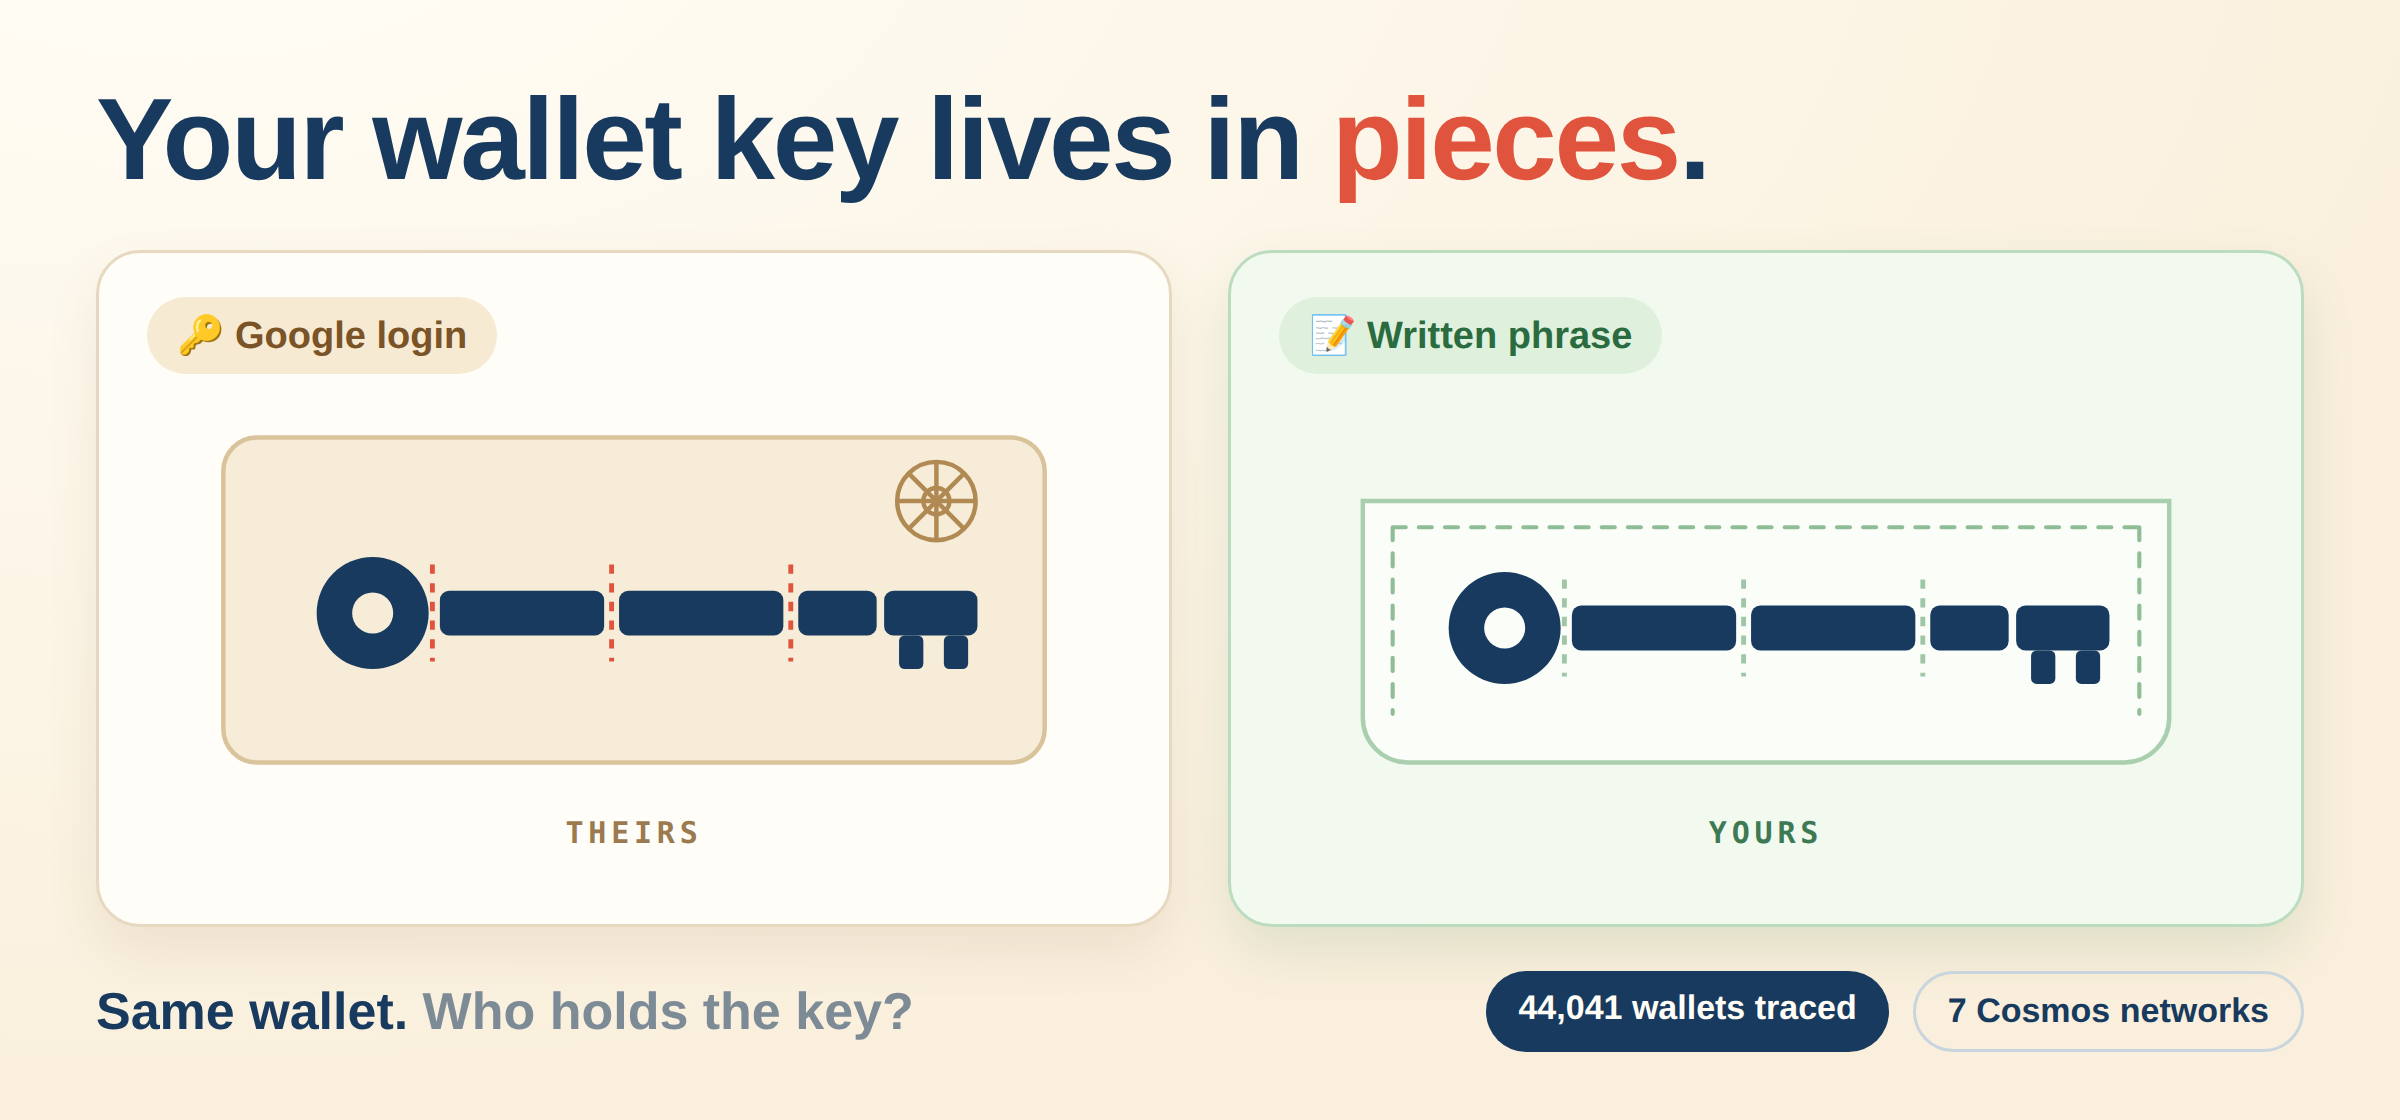
Who holds the pieces of your key?
| how you made it | who holds the key | a breach there reaches |
|---|---|---|
 Google / Apple login |
shares held on the provider’s side | every wallet behind it |
 Seed phrase |
the paper in your drawer | one phrase, one wallet |
 Hardware wallet |
the device in your hand | one device, one wallet |
The convenience was the exposure: no phrase to lose, and no phrase to hold.
Tonight, in four moves
 Check the published list — Keplr’s verified recovery addresses cover 11 Cosmos chains and one EVM address across 8 EVM chains (Nov 8, 06:31 UTC).
 Google and Apple login stay off — Web3Auth’s status page shows the login service in maintenance, and a seed-phrase or hardware account carries on exactly as before.
 Move liquid assets out of any Google or Apple Keplr account, and keep new funds out of that account.
 Check through the teams only — Keplr is building its affected-account checker; every “check your wallet” page and DM offering recovery this week is bait.
🔎 The full timeline, the tracing, and the one number nobody has
The timeline
- Nov 6, 20:52 UTC — the first sweep lands on chain, 21 minutes before the first notice.
- Nov 6, 21:13 UTC — Web3Auth discloses a security issue, pauses the embedded wallet service, and reports no evidence that MetaMask users are impacted.
- Nov 7, 04:38 UTC — Keplr reports unauthorised transactions on accounts created with Google or Apple, flags them to Web3Auth, and switches both logins off.
- Nov 7, 05:18 ET — a Cosmos Hub batch turns 2,265.59 staked ATOM from six accounts into transferable staking claims, with the memo
lsm recovery batch— the forum report names the delegator. - Nov 7, 17:17 UTC — Keplr names the cause: a Web3Auth infrastructure vulnerability that exposed private keys.
- Nov 8, 06:31 UTC — Keplr publishes the verified recovery-address list.
The numbers, each with its owner
- 44,041 wallets on seven Cosmos chains plus 7,603 on Injective sent funds to two addresses that held $6.01M by 15:38 UTC on Nov 7 — Bitquery’s balance snapshot, a floor rather than a total.
- Those two addresses are the ones Web3Auth published as its recovery wallets; Bitquery called them attacker collectors, and the attribution stays open.
- 86% of the traced funds left after Keplr’s 04:38 warning — pausing a login protects fresh logins, not keys already out.
- 1.96M staked ATOM moved without the 21-day unbonding, through tokenized shares; median loss $1.34, largest $325K, and 81,006 USDC on Noble sits where Circle can freeze it.
- Josh Lee’s early estimate: ~20% of Google and Apple accounts. Keplr and Web3Auth have published no confirmed total.
What is still open
- No CVE, no root-cause write-up, no audit, and no confirmed loss total from either company.
- The design is the story: two of the three key shares sit on the provider’s side, and its nodes hold the key that unlocks a third. A breach on that side meets the threshold without touching your device. Web3Auth has not said which component failed.
- Dungeon Wallet is the second app named on the list, and Lava Network issued its own alert.
- A delegator can start unbonding and revoke
authzfrom a compromised address;disable-tokenize-shares(docs) is the setting to hold before an incident, since switching it back takes the full 21 days. - Rescue transfers look exactly like drains, which is why balances vanished from wallets that were being protected.
Sources: Web3Auth’s status page and disclosures · Keplr’s notices (Nov 7–8) · Bitquery’s investigation · MetaMask Embedded Wallets docs.
Plus Cosmos liquid-staking docs · the Cosmos Hub forum report · crypto.news · cybersixt · 0xCERT · KuCoin News · The Defiant.
What do you guys think — was “log in with Google” for a wallet always going to end like this, or is this one provider’s bad week?
And be honest: how many of your wallets were made with a social login instead of a seed phrase?
 !