 Root your Android WITHOUT unlocking the bootloader — gone on reboot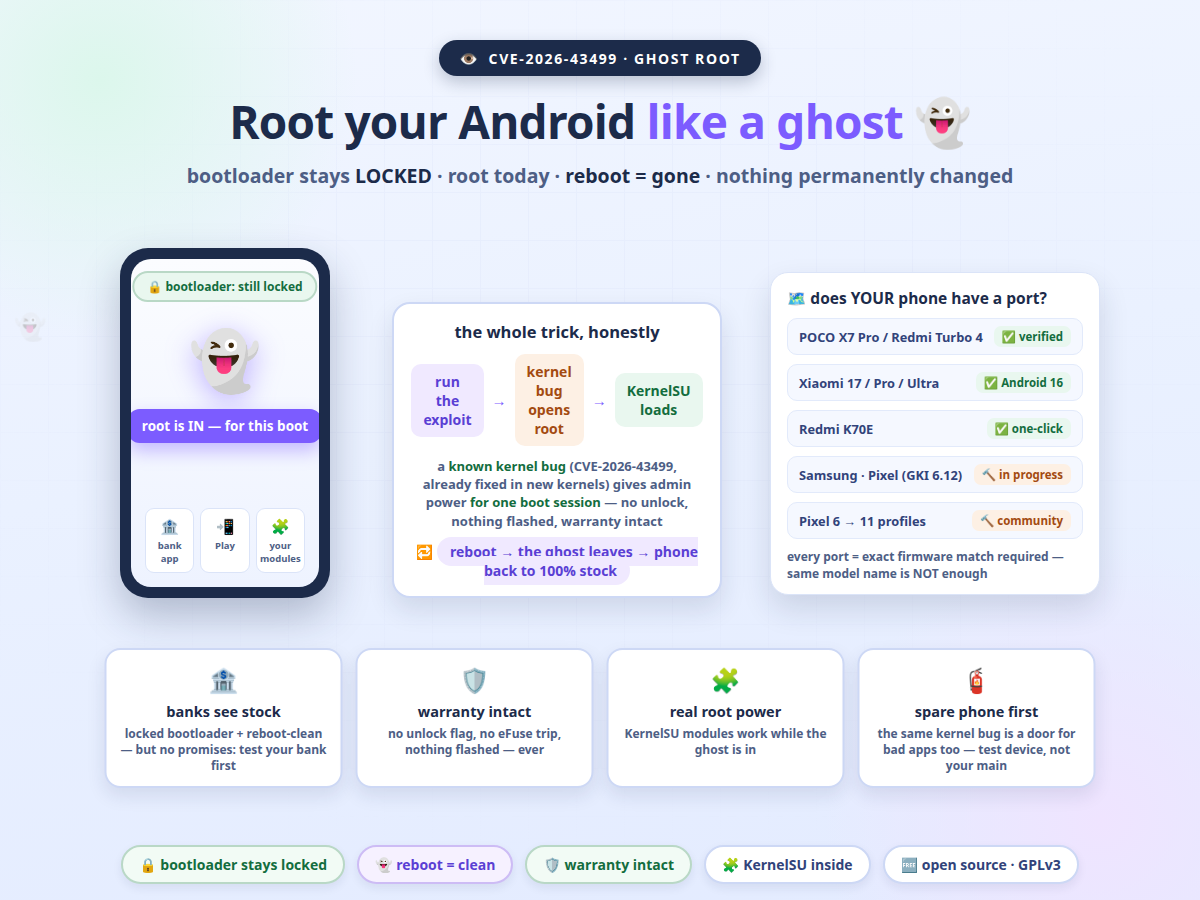
no unlock · no flash · no traces · reboot = back to stock
a public kernel bug (CVE-2026-43499) gives admin power for one boot session, with KernelSU riding along — this is the open-source project that packs it into one run (542 , GPLv3)
  [LOCKED PHONE] ──▶ [KERNEL BUG] ──▶ [ROOT · TODAY]
   bootloader         one public       KernelSU loads
   stays locked       CVE, run once    gone on reboot
▁ ▂ ▃ what the ghost can do ▃ ▂ ▁
 KernelSU modules — real root powers while the session lasts, no bootloader touched
 banks see a stock phone — locked bootloader, reboot-clean… but that’s “usually”, not a promise: test your bank first
 warranty stays intact — no unlock flag, no eFuse trip, nothing flashed, ever
▁ ▂ ▃ does your phone have a ghost? ▃ ▂ ▁
| phone | ghost status |
|---|---|
 POCO X7 Pro / Redmi Turbo 4 |
 the verified target (repo) |
 Xiaomi 17 / Pro / Ultra |
full Android 16 port (popsicle) |
 Redmi K70E |
one-click flow (duchamp-root) |
 Samsung · Pixel (GKI 6.12) |
 in progress (S26) |
 Pixel 6 → 11 |
community profiles (Root My Pixel) |
same model name is NOT enough — every port needs your exact firmware build, matched by hash
▁ ▂ ▃ the honest fine print ▃ ▂ ▁
 reboot = clean — the ghost leaves, stock returns, unroot = reboot + delete payload + revoke ADB
 the bug cuts both ways — until your kernel is patched, that same door exists for bad apps: use a spare phone, not your main one
 banks: usually, not guaranteed — hardware checks on Android 13+ can still notice a modified session (Play Integrity)
 images come from official OEM packages only — Google’s OTA sideload needs no unlock; wrong-firmware experiments are how bricks happen
Root like a ghost: in, do the thing, reboot — and the phone never knew.
 !